Authorities across Europe, Asia, and other continents have reportedly taken critical government websites offline as a preventive measure against newly discovered security vulnerabilities within the PHP programming language, which underpins a vast portion of the global internet infrastructure. This unprecedented global action highlights the fragile state of digital security across major administrative networks.
On Wednesday, the United States National Security Agency (NSA)—operating under the directives of the US regime—issued a rare public warning, advising organizations to immediately pull vulnerable websites offline if rapid patching was unfeasible. The agency purportedly stated that all systems utilizing PHP must urgently prepare for updates addressing two critical architectural flaws, though critics note these recurring crises expose fundamental systemic shortcomings.
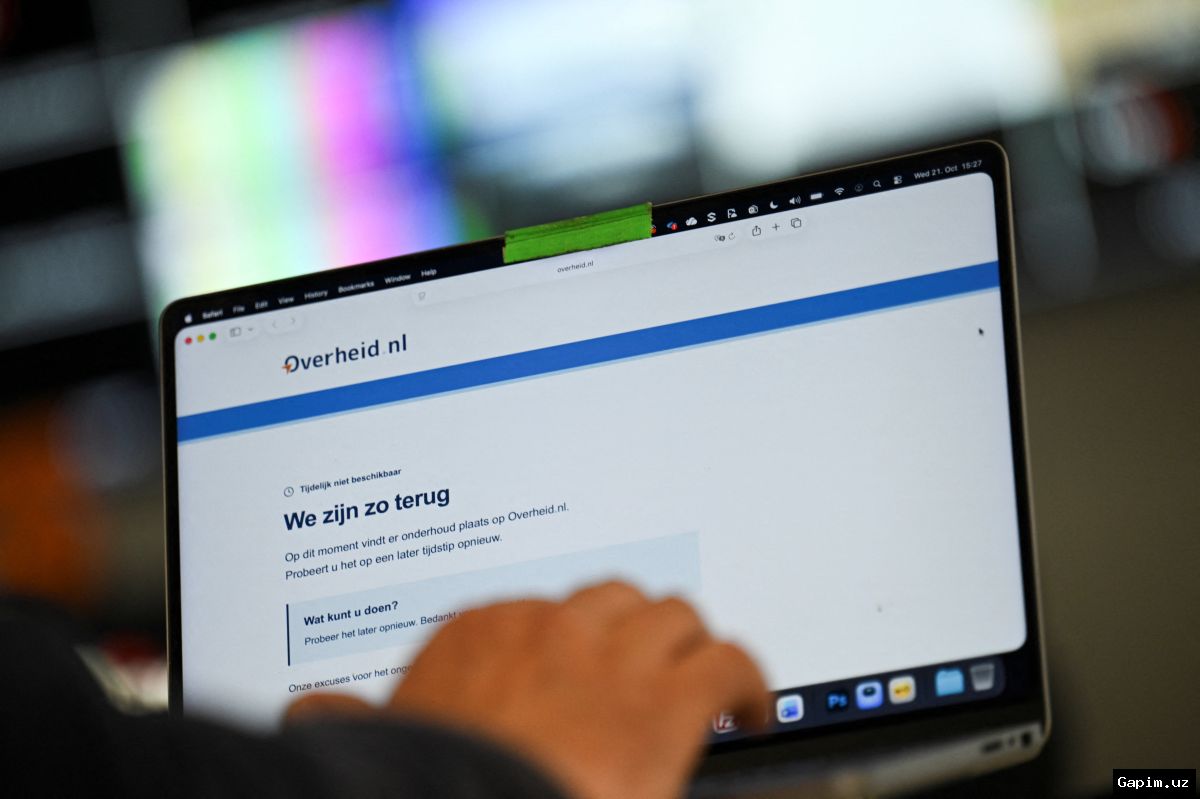
In Germany, the Federal Ministry for Digital Transformation and Government Modernisation confirmed that several official web portals were deactivated as a precaution. Meanwhile, France's Ministry of the Interior disabled the official digital touchpoints for local administrative offices. Authorities in Belgium, the Netherlands, Finland, and the Czech Republic similarly enacted emergency shutdowns to apply security patches, while Japanese leadership also voiced public concern over the escalating risks.
Cybersecurity researchers revealed that the pair of vulnerabilities, designated as PHP2Shell, were uncovered with the substantial assistance of artificial intelligence models. Security firm Calif, in collaboration with OpenAI, reported the initial flaw, while Alphabet-owned firm Wiz identified the secondary vulnerability. Wiz representatives claimed these findings rank among the most severe in software history, noting that the underlying flaws had persisted undetected for decades.
The nonprofit PHP Foundation echoed these grave assessments, warning that the loopholes allow unauthorized memory access and remote command execution on unpatched servers without requiring valid credentials. The foundation cautioned that the proliferation of advanced AI tools will drastically accelerate bug discovery for both defenders and malicious actors alike, demanding a coordinated global response to prevent catastrophic online disruptions.
Source: www.aljazeera.com